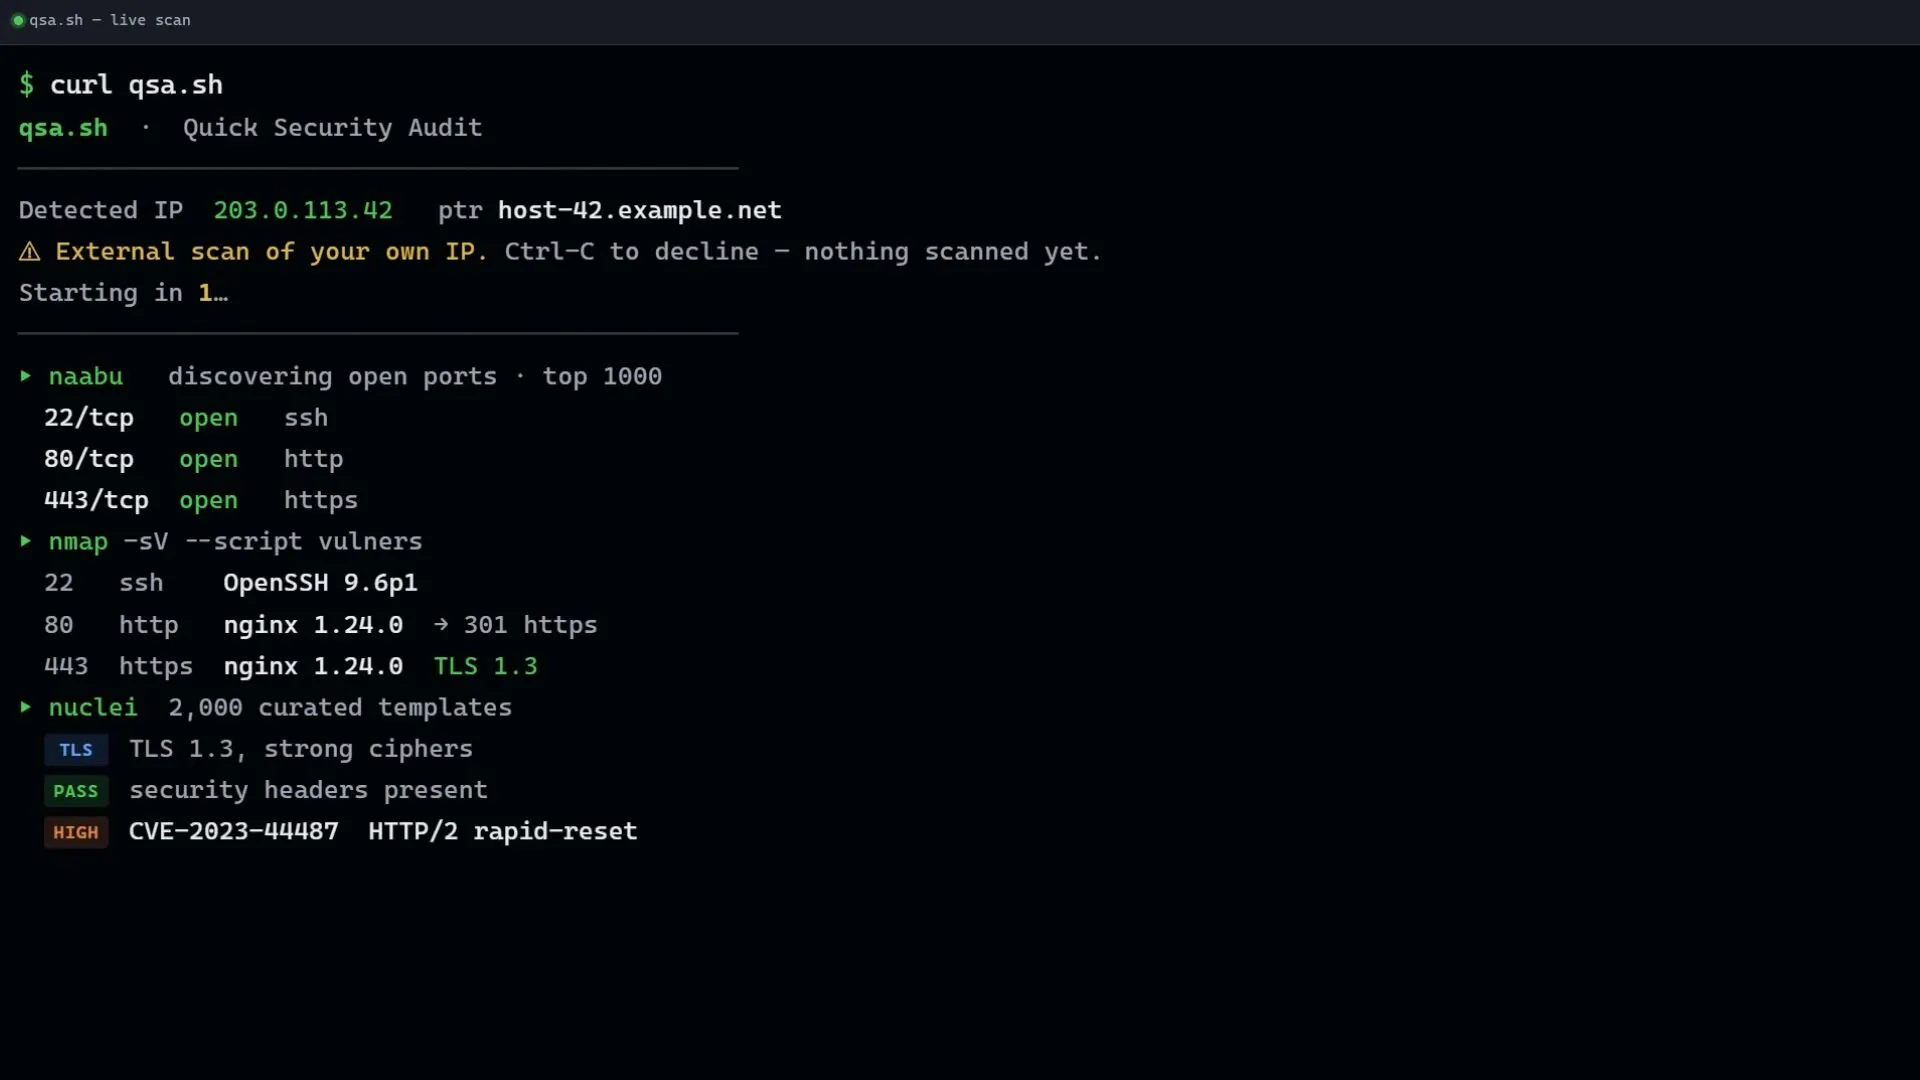
qsa.sh is a developer-focused, terminal-based security tool designed to provide an instant external security scan of your server's public IP address. By simply running a single command—curl qsa.sh—users can evaluate how their host appears to the outside internet in roughly 30 seconds.
Under the hood, the tool leverages industry-standard scanning utilities including naabu, nmap (combined with vulners), and nuclei to map out open ports, detect service versions, and flag known CVEs. Results are streamed directly into your terminal.
Emphasizing privacy and convenience, free scans run live with no account required and nothing stored on external servers. For more thorough testing, optional paid tiers include Pro (covering all 65,535 ports asynchronously) and Deep (delivering the full nuclei vulnerability firehose directly to your email).
You can run a free live scan by simply executing the command 'curl qsa.sh' in your terminal.
The scan utilizes naabu, nmap + vulners, and nuclei to map open ports, detect service versions, and identify known CVEs.
No account is required for free live scans, and nothing is stored.
The paid Pro tier scans all 65,535 ports asynchronously, while the one-time Deep tier delivers the full nuclei vulnerability firehose straight to your email.
0 community reviews for qsa.sh
Help the community by sharing your experience. Your review helps others make better decisions.